Talk
Intermediate
MIT License
LLM Security in Practice: Real Exploits, Real Defences
Proposal status is Rejected
References
Session Categories
Engineering practice - productivity, debugging
Talk License:
MIT License
Which track are you applying for?
Security
Speakers
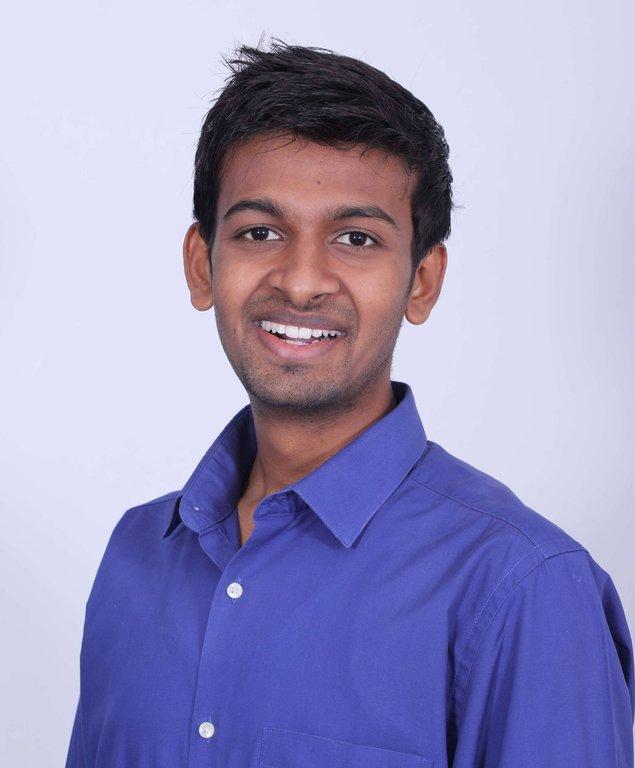
Jeevan D C
Senior Principal Engineer | Entain
Jeevan D C is a builder and architect who's been automating his way out of boredom since 2015.
He wrote the first line of code for a digital bank that scaled to 1.5 million customers, helped grow the engineering organization from 3 to 300 people, and led a cloud migration with just 4 hours of downtime.
Over the years, he's worked across banking, telecom, insurance, and gaming — designing systems for scale and then fixing the organizational structures around them.
He teaches at HyperVerge Academy, speaks at conferences, and runs a 2k+ member tech community.
These days, he's focused on technology strategy, organizational design, and occasionally breaking LLMs for fun.