The Identity You Didn't Know You Granted: How MCP Quietly Breaks Per-User RBAC in LLM-Powered SOC Tools
References
Session Categories
Which track are you applying for?
Speakers
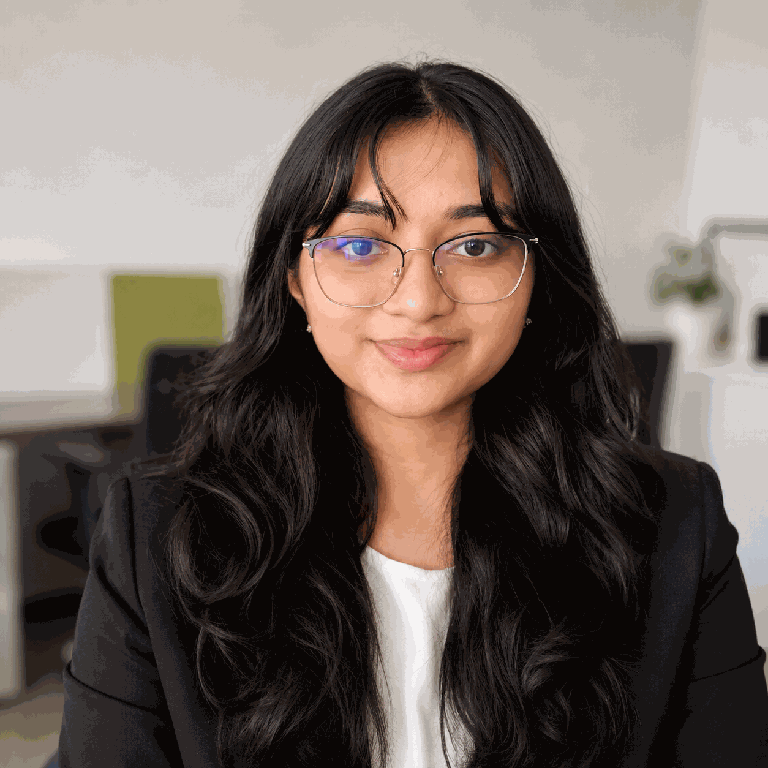
Maithily Rajpure is a Computer Engineering student specializing in Cybersecurity and an AI Engineering Intern at IIT Bombay's Trust Lab, where she works on secure AI systems for Security Operations Centers (SOCs). Her work focuses on LLM security, authorization, trust boundaries, and building practical AI-powered security tooling.
She is a contributor to queryCopilot, an open-source Kibana plugin that enables analysts to investigate security logs using natural language. While building it, her team uncovered subtle but critical security flaws involving MCP-based architectures, identity propagation, authorization bypasses, and prompt injection in real-world SOC workflows.
At DevRoom, Maithily will share lessons learned from breaking and hardening their own system, demonstrating why the biggest security risks in AI-powered infrastructure often come not from the model itself, but from overlooked assumptions about identity, permissions, and trust boundaries.
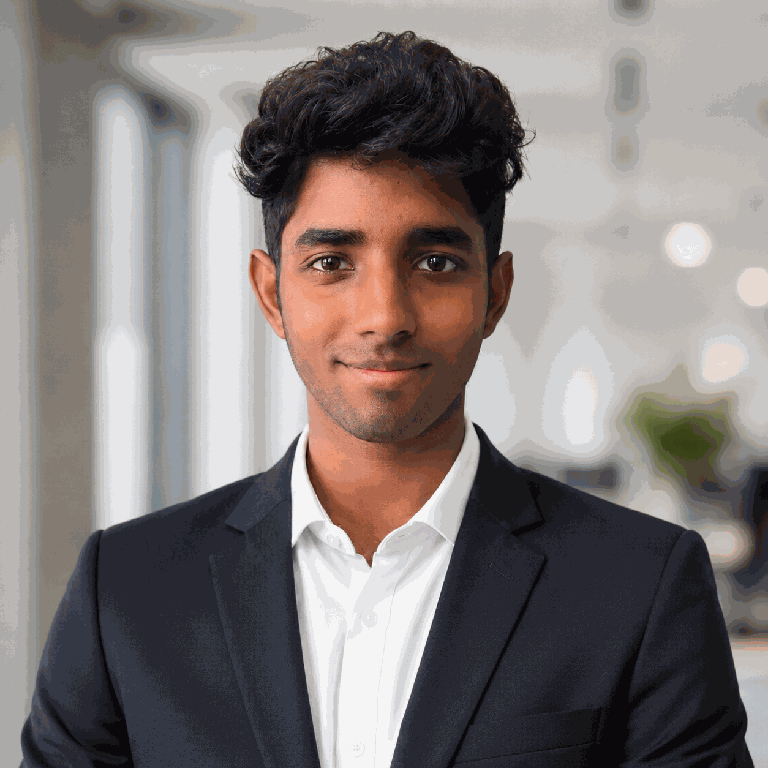
Harshit Gupta is a Full Stack Developer and Computer Science student specializing in Mobile and Web Application Development, with a strong interest in application security, AI systems, and developer tooling. He has worked on building AI-powered applications and security-focused platforms, including queryCopilot, an open-source Kibana plugin that enables natural language querying of Elasticsearch through LLMs and the Model Context Protocol (MCP).
His work focuses on understanding the trust boundaries introduced by AI integrations, particularly where authentication, authorization, and user-controlled input intersect with large language models. Through hands-on research and offensive testing of his own systems, he explores how seemingly ordinary engineering decisions can create significant security risks in LLM-powered applications.
At this session, Harshit shares practical findings from building and breaking real-world AI security tooling, demonstrating how identity propagation failures, authorization gaps, and prompt injection risks emerge in modern SOC environments—and, more importantly, how to fix them.