Skip to Main Content
Talk Intermediate

The Open Source Dependencies Running Your Startup (Without You Knowing It)
Proposal status is Rejected
Srinithi L
Srinithi L
Session Description

Modern applications are built on open source. Whether it's a web application, mobile backend, AI service, or cloud platform, developers routinely install a handful of packages and move on. What often goes unnoticed is the vast dependency graph hidden underneath those direct dependencies.

A single package installation can introduce hundreds of transitive dependencies, each maintained by different individuals, governed by different release cycles, and carrying different levels of risk. Over the years, attackers have exploited this complexity through dependency confusion attacks, typosquatting, malicious package updates, and compromised maintainer accounts.

This talk explores the hidden software supply chain that powers modern applications. Through real-world incidents and practical demonstrations, attendees will learn how dependency trees evolve, how supply-chain attacks work, and why organizations increasingly treat dependency management as a critical security concern.

The session will also introduce open-source tools that help developers audit dependencies, generate Software Bills of Materials (SBOMs), identify vulnerabilities, and integrate dependency checks into CI/CD pipelines.

By the end of the talk, attendees will have a practical framework for understanding, visualizing, and securing the open-source ecosystem their applications depend upon.

Session Outline

  1. The Dependency Graph Nobody Sees

    • Direct vs transitive dependencies

    • Visualizing dependency trees

    • Why dependency count grows rapidly

  2. When Dependencies Become Security Risks

    • Dependency confusion

    • Typosquatting

    • Malicious package releases

    • Real-world supply chain incidents

  3. Securing the Open Source Supply Chain

    • Vulnerability scanning

    • SBOM fundamentals

    • Dependency auditing

    • CI/CD integration

  4. Practical Checklist for Teams

    • What to audit today

    • Recommended open-source tools

    • Secure dependency management practices

Key Takeaways

• Understand how modern applications accumulate large dependency chains.

• Learn the difference between direct and transitive dependencies and their associated risks.

• Explore real-world examples of open-source supply-chain attacks.

• Discover open-source tools for dependency auditing, SBOM generation, and vulnerability detection.

• Leave with actionable practices to improve dependency security in personal projects, startups, and production systems.

References

Session Categories

Technology architecture
Engineering practice - productivity, debugging

Which track are you applying for?

Main track

Speakers

Srinithi L
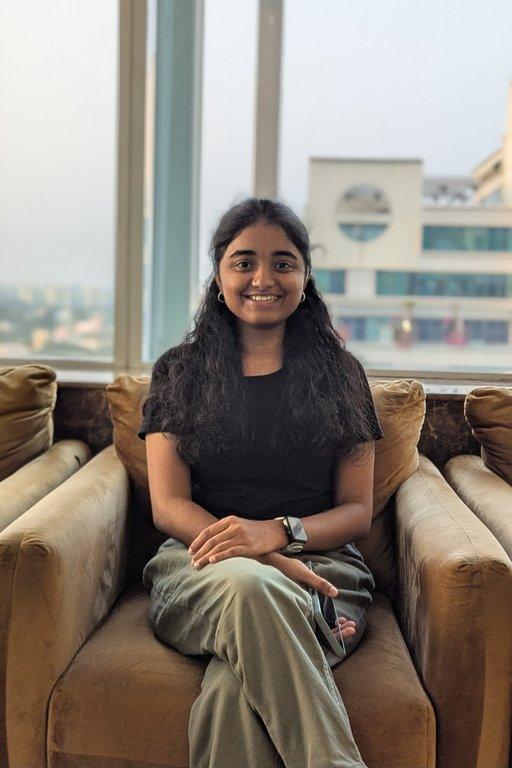
Srinithi L Software Engineer | HCL GUVI

Srinithi Loganathan is a software developer, tech speaker, and open-source contributor passionate about building impactful technology and fostering developer communities. She has worked on projects across web technologies, cloud platforms, and community-driven initiatives, with a strong interest in software architecture, security, and open-source ecosystems.

Srinithi is a Smart India Hackathon winner and has spoken at developer events, sharing practical engineering insights and real-world experiences with the tech community. As an advocate for open collaboration and knowledge sharing, she actively contributes to community initiatives and enjoys exploring how open-source technologies power modern software systems.

Through her work and talks, she aims to help developers build secure, scalable, and maintainable applications while encouraging greater participation in the open-source ecosystem.

Linkedin: https://www.linkedin.com/in/srinithiloganathan/